 Cloudflare · @cloudflare ↗
Security Audit
Cloudflare's single-repo security auditing skill for coding agents, combining six-phase multi-agent vulnerability hunting, adversarial verification, and zero-dependency JSON validators.
The roster
What it does
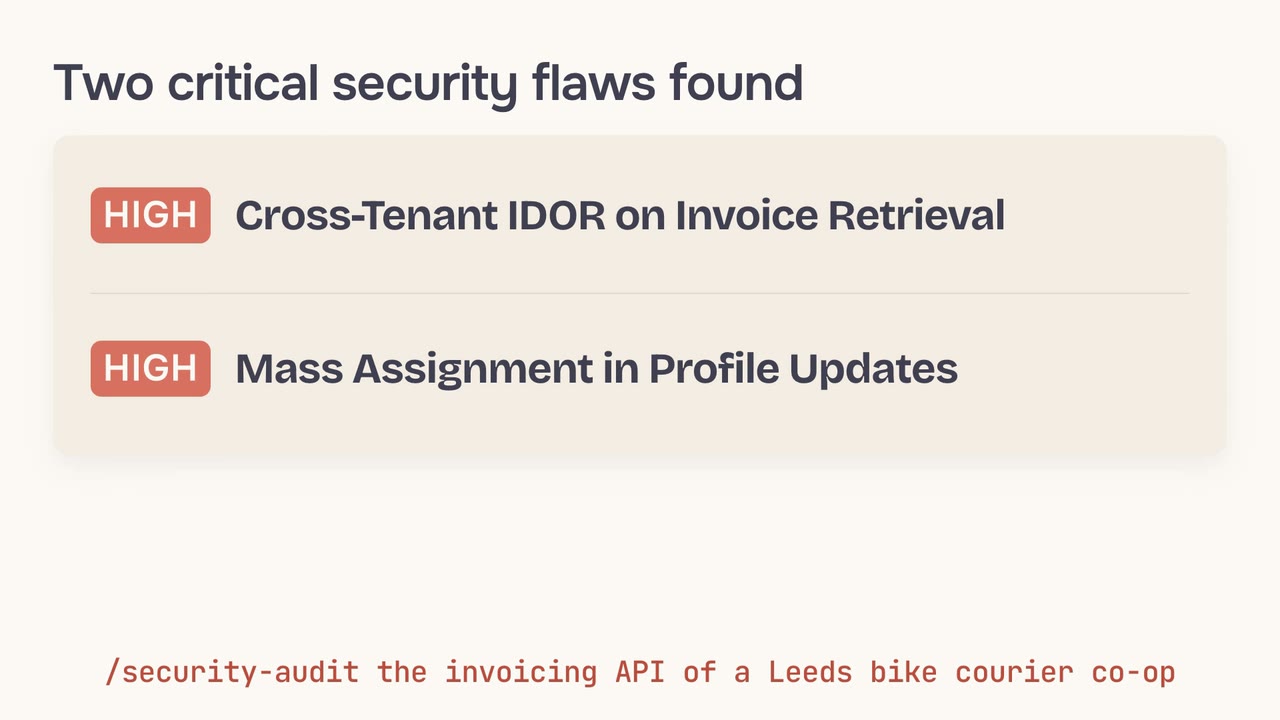
Security Audit is Cloudflare's open-source coding-agent skill that turns your agent into a structured vulnerability auditor for codebases, APIs, services, CLI tools, libraries, and daemons. Originally built as the single-repository starting point for Cloudflare's internal vulnerability discovery system, it packages the prompts, schemas, and validators needed to run repeatable source-first security reviews.
The repository ships one comprehensive skill made of 15 markdown instruction and domain-companion files—covering web protocols, AI and LLM apps, memory safety, cloud infrastructure, supply chain, client-side code, RPC messaging, data isolation, resource exhaustion, and local IPC—alongside report-schema.json and two zero-dependency Node.js validators for findings and coverage ledgers. It works with any coding agent that supports tool use and parallel sub-agents.
When to use it
- You want your coding agent to run structured security reviews
Install the skill with the Skills CLI so your agent can answer focused security questions in guidance mode or run six-phase repository audits on demand.
- You audit targets across web, cloud, native, or AI stacks
Pull in ten specialized domain companions that guide hunters through stack-specific trust boundaries, from LLM tool-calling and IAM policies to C memory safety.
- You need machine-checkable audit outputs across multiple runs
Validate every run with the bundled Node.js scripts and JSON schemas so coverage ledgers and confirmed findings stay consistent from commit to commit.
Common questions
How do I install the Security Audit collection?
Install it through the Skills CLI by running npx skills add https://github.com/cloudflare/security-audit-skill --skill security-audit, or add the --global flag to make it available across all of your projects.
Which coding agents does it work with?
Security Audit is agent-neutral and works with any coding agent that supports tool use and parallel sub-agent delegation, alongside a local Node.js installation for running its schema and coverage validators.
Is it free and open source?
Yes. Cloudflare releases the repository under the MIT license with zero external npm dependencies, so you can inspect, run, and adapt all prompts, attack-class companions, and validator scripts for free.